Cookies Privacy
I accept Cookies Policy We use cookies to understand how you use our website and to improve your experience. By continuing to use this website, you accept our Link is copied!

Vulnerability Assessment

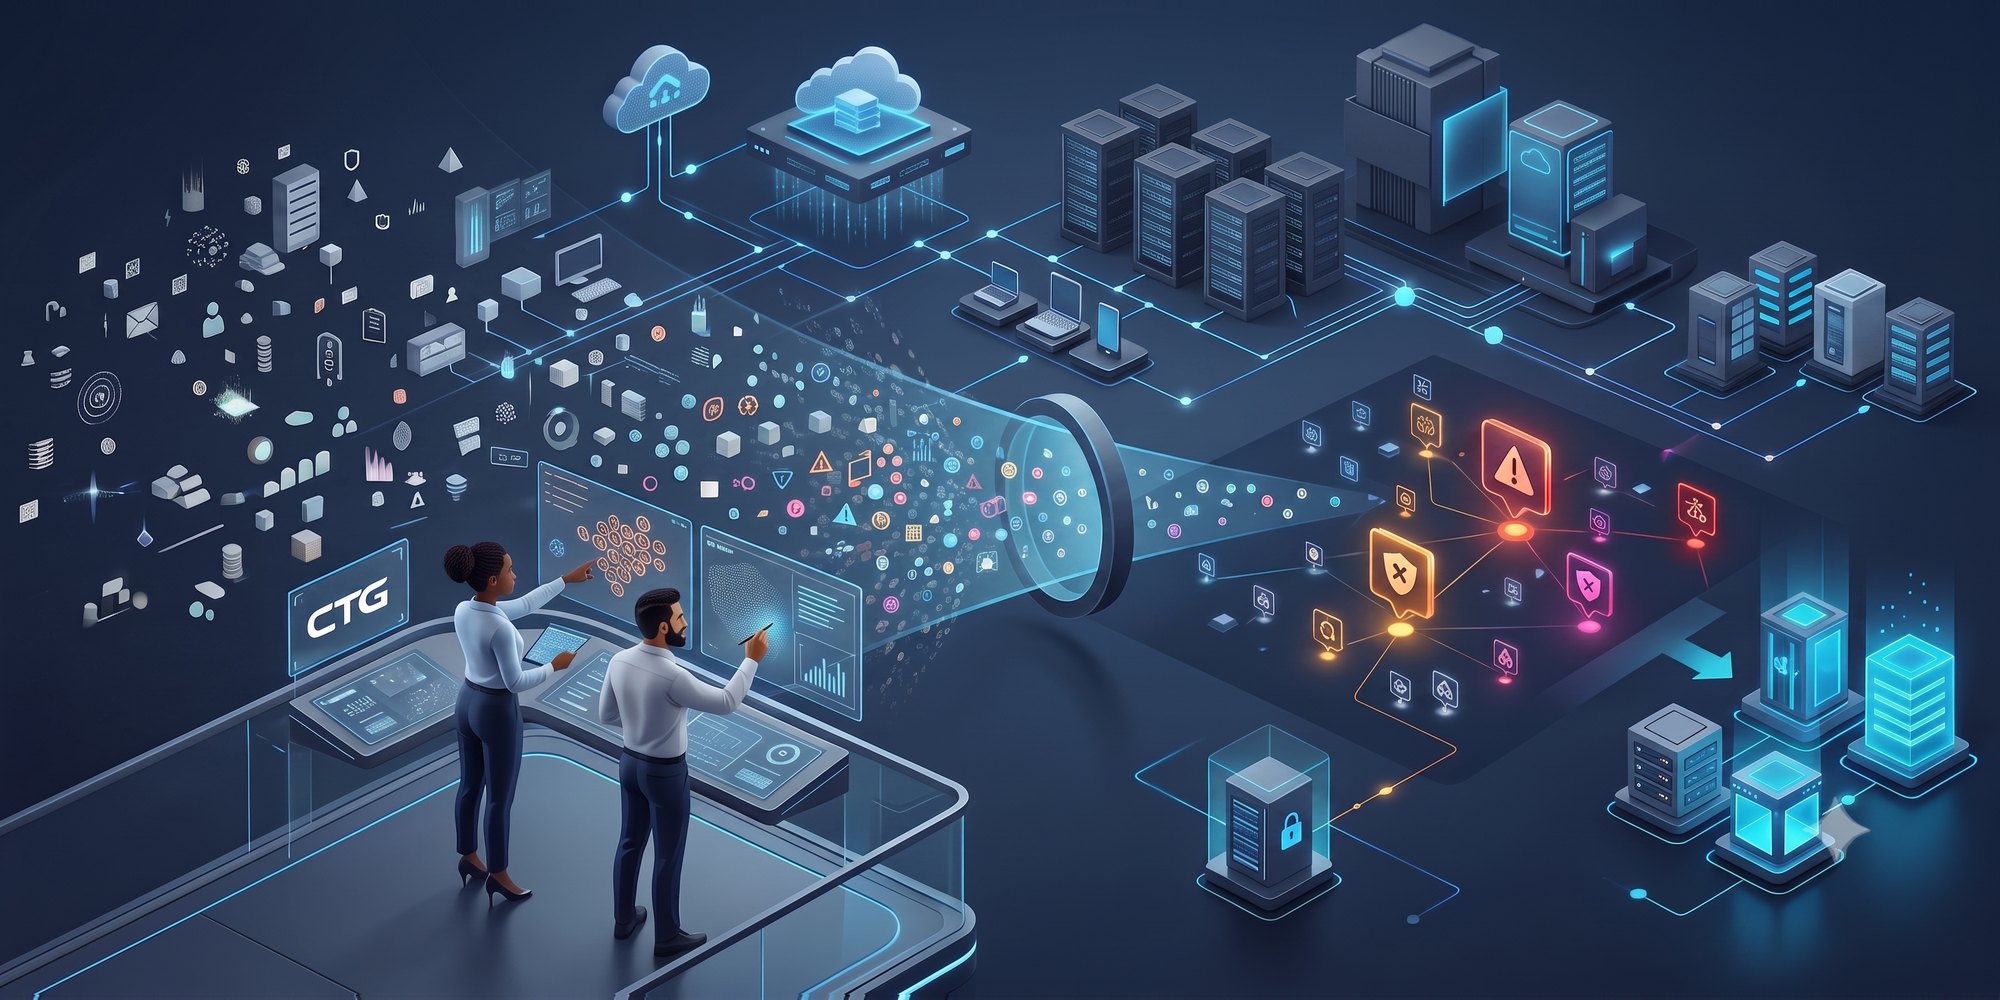
A vulnerability assessment discovers known weaknesses, validates material findings and prioritises remediation according to exposure, exploitability and business impact. It is suitable for organisations that need a reliable technical baseline, recurring assurance or broader coverage than a penetration test can provide within the same period.

What this service helps you achieve?

The purpose is to replace unprioritised findings with a current view of exploitable exposure and accountable remediation.

  • Improve visibility of known weaknesses across authorised assets.
  • Reduce false positives through expert review and contextual validation.
  • Prioritise remediation using more than scanner severity alone.
  • Identify unsupported systems, weak configurations and recurring patterns.
  • Create a repeatable baseline for remediation tracking.


Scope: what we examine?

Scope is fixed with you before any work starts. Depending on the objective, environment and authorised access, the engagement may cover:

  • External and internal network assets.
  • Servers, workstations and common operating systems.
  • Web services, databases and infrastructure applications where supported.
  • Authenticated and unauthenticated scanning.
  • Cloud-hosted assets and authorised public endpoints.
  • Missing patches, insecure services and known vulnerabilities.
  • Configuration observations visible to the assessment tools.
  • Validation of high-impact findings and remediation priorities.

Our approach, step by step

Agree asset ownership, scanning windows, credentials, exclusions and operational safeguards.

1. Confirm asset scope:

Use appropriate authenticated and unauthenticated methods to improve coverage.

2. Discover and scan:

Review high-risk results, remove obvious false positives and confirm affected assets.

3. Validate material findings:

Consider exploitability, exposure, business criticality, compensating controls and fix availability.

4. Prioritise remediation:

Provide a baseline and, where agreed, support later validation or recurring assessment.

5. Report and track:

Deliverables you can act on

Everything we hand over speaks to both leadership and the people who will act on it. Depending on scope, they may include:

  • Asset and coverage summary.
  • Validated vulnerability register.
  • Executive risk overview.
  • Technical findings with affected assets and evidence.
  • Prioritised remediation plan.
  • Observations on recurring root causes and unsupported technology.
  • Optional reassessment results.

How CTG keeps the work focused?

Asset ownership, data quality and prioritisation criteria are agreed before analysis. Findings are validated, grouped by root cause and linked to remediation owners so that the output does not become an unmanageable list of vulnerabilities.

When this service is the right choice?

  • A reliable vulnerability baseline is missing.
  • The organisation needs broad asset coverage.
  • Patch and remediation teams need prioritised input.
  • A new environment or acquisition must be assessed.
  • Regulatory or customer requirements call for recurring assessment.
  • Penetration testing needs a broader discovery foundation.

Standards, timing and service boundaries

The engagement may draw on CVSS used with contextual risk factors, CISA Known Exploited Vulnerabilities where relevant, CIS and vendor guidance, applicable customer policies. Referencing a framework describes how we structure the work; it is not, in itself, a certification, accreditation or regulatory ruling.


Timelines are set once scope is agreed, and vary with the size of the environment and the availability of evidence and stakeholders.


A vulnerability assessment is not the same as penetration testing. It primarily identifies known weaknesses and visible configuration issues; it does not automatically demonstrate complete attack paths or eliminate the need for manual testing.
Discuss Vulnerability Assessment with CTG. A short scoping session confirms the objective, boundaries, evidence, delivery model and outputs before we issue a proposal.

Related services

Frequently asked questions

What does Vulnerability Assessment cover?

Scope is fixed with you before any work starts. Typical areas include external and internal network assets, Servers, workstations and common operating systems, Web services, databases and infrastructure applications where supported, and Authenticated and unauthenticated scanning. Exclusions, required access, your responsibilities and acceptance criteria are all set out in the proposal.

What will we receive at the end of the engagement?

Deliverables depend on the agreed objective and may include asset and coverage summary, Validated vulnerability register, Executive risk overview, and Technical findings with affected assets and evidence. Every significant finding is tied to evidence, business impact, priority and a clear owner for the next step.

How is this different from penetration testing?

Exposure management identifies, validates and prioritises weaknesses across a defined estate. Penetration testing is a separate authorised exercise that attempts controlled exploitation to demonstrate realistic attack paths.

How are findings prioritised?

Priority should reflect exploitability, asset criticality, exposure, threat activity, control effectiveness, business impact and remediation dependencies - not severity scores alone.

How long does the engagement take?

Timelines are set once scope is agreed, and vary with the size of the environment and the availability of evidence and stakeholders.

How does this relate to External Attack Surface Management?

These services answer related but distinct questions. Scoping identifies whether Vulnerability Assessment, External Attack Surface Management, or a coordinated programme is the smallest useful approach without duplicating work.

What are the principal limitations?

A vulnerability assessment is not the same as penetration testing. It primarily identifies known weaknesses and visible configuration issues; it does not automatically demonstrate complete attack paths or eliminate the need for manual testing.